SQL injection in a non-web application
Possible duplicate:
Non-SQL Injection Interface
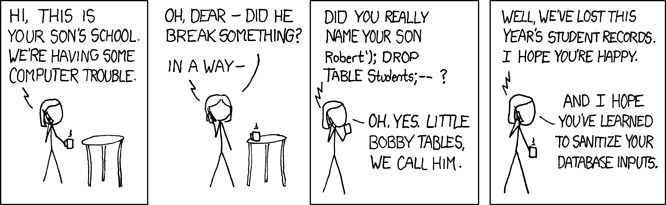
Does anyone know of a good example of a SQL Injection vulnerability that is missing from a web application? What does the user enter for this attack? I'm looking for real vulnerability, not speculation. The following picture is an example of an alleged attack.
alt text http://leonardoanceschi.files.wordpress.com/2008/05/mini.jpg
a source to share
SQL injection is available wherever sql queries are generated from input without any sensitive character escaping (like '
). so if you have a desktop application that takes an input textbox and generates a sql query string using it, you can have an injection attack vector.
it has nothing to do with being in a web context.
a source to share
SQL Injection is more visible in web applications because they are publicly available, but in particular it has nothing to do with it. Anytime you don't parameterize your SQL queries, you run the risk of injection attacks.
If your console or WinForms application takes the username and fetches from the database to see if the user exists, and this is done by concatenating strings to create an SQL query, you are at the same risk. Always parameterize or avoid your SQL queries properly!
a source to share